Act now and download your HP HPE6-A82 test today! Do not waste time for the worthless HP HPE6-A82 tutorials. Download Avant-garde HP Aruba Certified ClearPass Associate Exam exam with real questions and answers and begin to learn HP HPE6-A82 with a classic professional.
Also have HPE6-A82 free dumps questions for you:
NEW QUESTION 1
What are two ways to add guest accounts to ClearPass? (Select two.)
- A. Using the "Import Accounts" under ClearPass Guest
- B. Using the "Create Account" or "Create Multiple'' options under ClearPass Guest
- C. Assigning the default role "Lobby Ambassador to a receptionist to then add the accounts
- D. Using the "Sync Accounts'' under ClearPass Guest
- E. importing accounts from Active Directory once ClearPass is added with Admin credentials
Answer: AB
NEW QUESTION 2
What services are recommended to be allowed by the pre-authenticated role assigned to the Client during the Captive Portal process? (Choose three.)
- A. DHCP options 43 and 150
- B. RADIUS to ClearPass
- C. HTTPS to ClearPass
- D. HTTPS to the Internet
- E. DHCP address assignment
- F. DNS resolution
Answer: CEF
NEW QUESTION 3
Which two are required to add a Network Access Device (NAD) into ClearPass? (Select two.)
- A. ClearPass Admin login credentials
- B. SSH password
- C. Shared Secret
- D. HTTPS certificate
- E. NAD IP address
Answer: CE
NEW QUESTION 4
A customer with 985 employees would like to authenticate employees using a captive portal guest web login page Employees should use their AD credentials to login on this page
Which statement is true?
- A. The customer needs to add second guest service in the policy manager for the guest network.
- B. The customer needs to add the AD server as an authentication source in a guest service
- C. Employees must be taken to a separate web login page on the guest network
- D. The customer needs to add the AD servers RADIUS certificate to the guest network.
Answer: B
NEW QUESTION 5
What is RADIUS Change of Authorization (CoA)?
- A. It allows ClearPass to transmit messages to the Network Attached Device/Network Attached Server (NAD/NAS) to modify a user’s session status
- B. It allows clients to issue a privilege escalation request to ClearPass using RADIUS to switch to TACACS+
- C. It is a mechanism that enables ClearPass to assigned a User-Based Tunnel (UBT) between a switch and controller for Dynamic Segmentation
- D. It forces the client to re-authenticate upon roaming to an access point controlled by a foreign mobility controller.
Answer: A
Explanation:
Referencehttp://www.arubanetworks.com/techdocs/ClearPass/Aruba_CPPMOnlineHelp/Content/CPPM_UserG
NEW QUESTION 6
What is the purpose of service rules in ClearPass? )
- A. selects the Posture Policy used with OnGuard
- B. selects the Enforcement Profiles used in a service
- C. selects the Service to process a request
- D. selects the Authentication Source for the client
Answer: D
NEW QUESTION 7
Which actions are necessary to set up a ClearPass guest captive portal web login page to execute with no errors? (Select two)
- A. Configure the vendor settings in the Web Login page to match the Network Access Device (NAD).
- B. Install a publicly signed HTTPS certificate in ClearPass and the Network Access Device (NAD).
- C. Install an enterprise Certificate Authority (CA) signed HTTPS certificate in the Network Access Device (NAD).
- D. Install an enterprise Certificate Authority (CA) signed HTTPS certificate in ClearPass and the Network D18912E1457D5D1DDCBD40AB3BF70D5DAccess Device (NAD).
- E. Configure the vendor settings in the Network Access Device (NAD) to match the web login page.
Answer: BE
NEW QUESTION 8
Your boss suggests configuring a guest self-registration page in ClearPass for an upcoming conference event. What are the benefits of using guest serf-registration'? (Select two)
- A. This will allow conference employees to pre-load additional device information as guests arrive and register.
- B. This strategy effectively stops employees from putting their own corporate devices on the guest network.
- C. This will enable additional information to be gathered about guests during the conference.
- D. This allows guest users to create and manage their own login account.D18912E1457D5D1DDCBD40AB3BF70D5D
- E. This will allow employee personal devices to be Onboarded to the corporate network
Answer: AD
NEW QUESTION 9
Which Authorization Source support device profile enforcement?
- A. Local user Repository
- B. Endpoint Repository
- C. OnGuard Repository
- D. Gust User Repository
Answer: A
NEW QUESTION 10
Select all that apply
Match the security description to the term that best fits. Options are used only once.
- A. Mastered
- B. Not Mastered
Answer: A
Explanation: 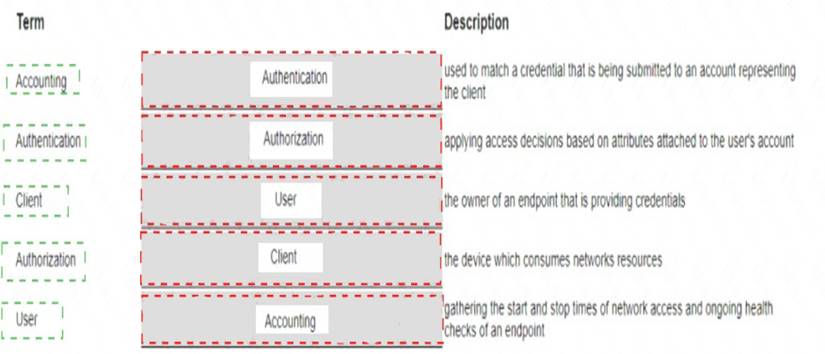
NEW QUESTION 11
When should a role mapping policy be used in an 802.1x service with Active Directory as the authentication source?
- A. When you want to match Active Directory attributes directly to an enforcement policy.
- B. When you want to enable attributes as roles directly without combining multiple attributes
- C. When you want to translate and combine Active Directory attributes into ClearPass roles.
- D. When you want to match Active Directory attributes to a Aruba firewall role on a Aruba Network Access Device.
Answer: A
NEW QUESTION 12
What happens when a client successfully authenticates but does not match any Enforcement Policy rules?
- A. A RADIUS Accept is returned and the default Enforcement Profile is applied.
- B. A RADIUS reject is returned for the client.
- C. A RADIUS Accept is retuned, and the default rule is applied to the device.
- D. A RADIUS Accept is returned with no Enforcement Profile applied
Answer: A
NEW QUESTION 13
What is the significance of using the [Allow ALL MAC AUTH] as an Authentication Method for Guests?
- A. This removes the reliance on the known or unknown status for MAC authentication.
- B. All clients with unknown endpoints will be granted guest access regardless of authorization
- C. Client attempts will fail without an additional Authentication method applied.
- D. All clients with known endpoints will be granted guest access regardless of authorization.
Answer: A
Explanation:
https://www.arubanetworks.com/techdocs/Instant_83_WebHelp/Content/Instant_UG/ Authentication/AuthenticationMethods.htm
NEW QUESTION 14
When using Guest Authentication with MAC Caching service template, which statements are true? (Select two.)
- A. The guest authentication is provided better security than without using MAC caching
- B. The guest authentication is provided better security than without using MAC caching
- C. The endpoint status of the client will be treated as "known" the first time the client associates to the network
- D. Which wireless SSID and wireless controller must be indicated when configuring the template
- E. The client will be required to re-enter their credentials even if still within the MAC-Auth Expiry term
Answer: AD
NEW QUESTION 15
Which fingerprint collectors can help to distinguish between an iPhone and an iPad? (Select two.)
- A. IF-MAP
- B. MAC OUI
- C. HTTP
- D. TCP header capture
- E. SNMP
Answer: AB
NEW QUESTION 16
Sponsorship has been enabled on the guest network A guest user connects and completes the self-registration form indicating a valid sponsor. The guest then clicks submit What is the current state of the guest account?
- A. The guest account is created in a disabled state with the "Log In" button grayed out
- B. The guest account is not yet created and remains in a disabled state There is not "Log in" button yet displayed
- C. The guest account is created in disabled state, the "Log In" button will appear only after the sponsor approval process is completed
- D. The guest account is created in an enabled state with the Tog in" button functional
Answer: C
NEW QUESTION 17
Refer to the exhibit.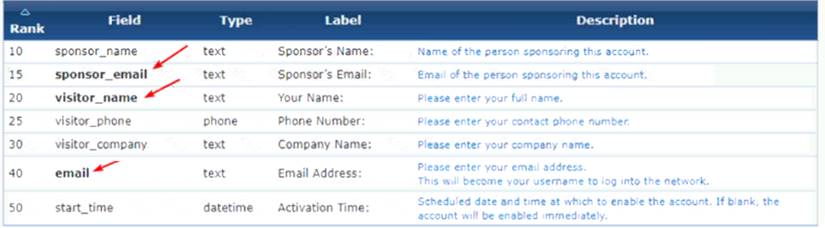
What does a bold field indicate?
- A. The field is currently enabled.
- B. The field is a non-system field
- C. The field has been customized
- D. The field Is required
Answer: B
NEW QUESTION 18
Which are valid enforcement profile types? (Select two)
- A. Policy Service Enforcement
- B. RADIUS Change of Authorization (CoA)
- C. Aruba Script Enforcement
- D. ClearPass Entity Update Enforcement
Answer: BD
NEW QUESTION 19
Which option support DHCP profiling for devices in a network?
- A. enabling DHCP relay on our network access devices so DHCP requests are forwarded to ClearPass
- B. enabling the DHCP server to profile endpoints and forward meta-data to ClearPass
- C. DHCP profiling is enabled on ClearPass by default configuration of the network access devices is not necessary
- D. configuring ClearPass as a DHCP relay for the client
Answer: A
NEW QUESTION 20
What are benefits of using Network Device Groups in ClearPass? (Select two.)
- A. Allows Service selection rules to match based upon which Network Device Group the Network Access Device (NAD) belongs to
- B. Network Access Devices (NADs) only require Aruba factory installed certificates to join a Network Device Group
- C. A Network Access Device is must be discovered by ClearPass prior to be added to a Network Device Group
- D. Another way to add a customizable "attribute" field to reference when processing authentication requests
- E. Can apply to both Network Access Devices (NADs) as wen as client machines as a way to filter authentication requests
Answer: D
NEW QUESTION 21
Which ClearPass feature assesses endpoint context and client device type?
- A. Profiling
- B. Posture
- C. Captive Portal
- D. Onboard
Answer: A
NEW QUESTION 22
......
Recommend!! Get the Full HPE6-A82 dumps in VCE and PDF From DumpSolutions.com, Welcome to Download: https://www.dumpsolutions.com/HPE6-A82-dumps/ (New 60 Q&As Version)