we provide Downloadable Cisco 200-201 free practice exam which are the best for clearing 200-201 test, and to get certified by Cisco Understanding Cisco Cybersecurity Operations Fundamentals. The 200-201 Questions & Answers covers all the knowledge points of the real 200-201 exam. Crack your Cisco 200-201 Exam with latest dumps, guaranteed!
Cisco 200-201 Free Dumps Questions Online, Read and Test Now.
NEW QUESTION 1
What is the virtual address space for a Windows process?
- A. physical location of an object in memory
- B. set of pages that reside in the physical memory
- C. system-level memory protection feature built into the operating system
- D. set of virtual memory addresses that can be used
Answer: D
NEW QUESTION 2
Refer to the exhibit.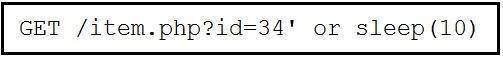
This request was sent to a web application server driven by a database. Which type of web server attack is represented?
- A. parameter manipulation
- B. heap memory corruption
- C. command injection
- D. blind SQL injection
Answer: D
NEW QUESTION 3
Which two elements are used for profiling a network? (Choose two.)
- A. total throughout
- B. session duration
- C. running processes
- D. OS fingerprint
- E. listening ports
Answer: DE
NEW QUESTION 4
Which evasion technique is a function of ransomware?
- A. extended sleep calls
- B. encryption
- C. resource exhaustion
- D. encoding
Answer: B
NEW QUESTION 5
What is the function of a command and control server?
- A. It enumerates open ports on a network device
- B. It drops secondary payload into malware
- C. It is used to regain control of the network after a compromise
- D. It sends instruction to a compromised system
Answer: D
NEW QUESTION 6
Which security technology allows only a set of pre-approved applications to run on a system?
- A. application-level blacklisting
- B. host-based IPS
- C. application-level whitelisting
- D. antivirus
Answer: C
NEW QUESTION 7
What is an attack surface as compared to a vulnerability?
- A. any potential danger to an asset
- B. the sum of all paths for data into and out of the application
- C. an exploitable weakness in a system or its design
- D. the individuals who perform an attack
Answer: B
NEW QUESTION 8
Which process is used when IPS events are removed to improve data integrity?
- A. data availability
- B. data normalization
- C. data signature
- D. data protection
Answer: B
NEW QUESTION 9
Which IETF standard technology is useful to detect and analyze a potential security incident by recording session flows that occurs between hosts?
- A. SFlow
- B. NetFlow
- C. NFlow
- D. IPFIX
Answer: D
NEW QUESTION 10
Refer to the exhibit.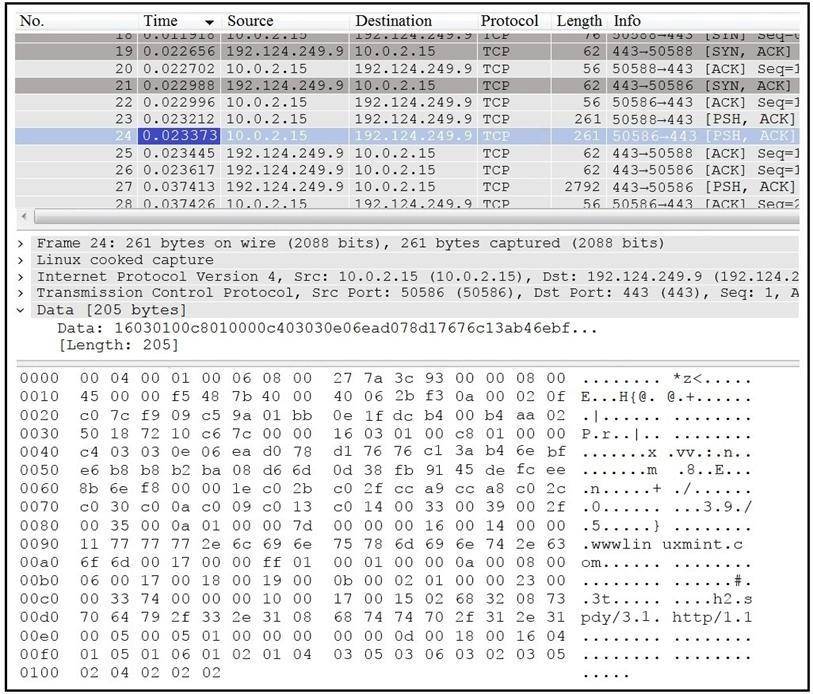
Which application protocol is in this PCAP file?
- A. SSH
- B. TCP
- C. TLS
- D. HTTP
Answer: B
NEW QUESTION 11
An analyst is exploring the functionality of different operating systems.
What is a feature of Windows Management Instrumentation that must be considered when deciding on an operating system?
- A. queries Linux devices that have Microsoft Services for Linux installed
- B. deploys Windows Operating Systems in an automated fashion
- C. is an efficient tool for working with Active Directory
- D. has a Common Information Model, which describes installed hardware and software
Answer: D
NEW QUESTION 12
Refer to the exhibit.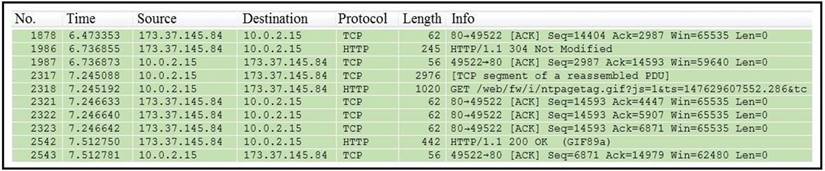
Which packet contains a file that is extractable within Wireshark?
- A. 2317
- B. 1986
- C. 2318
- D. 2542
Answer: D
NEW QUESTION 13
Refer to the exhibit.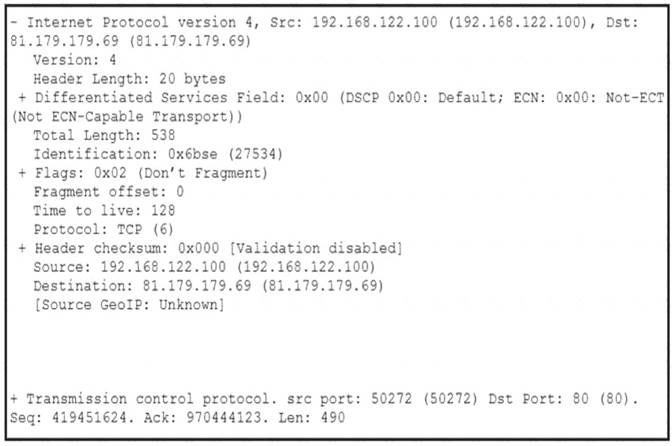
What should be interpreted from this packet capture?
- A. IP address 179.179.69/50272/192.168.122.100/80/6 is sending a packet from port 80 of IP address 192.168.122.100 that is going to port 50272 of IP address 81.179.179.69 using IP protocol 6.
- B. IP address 192.168.122.100/50272/81.179.179.69/80/6 is sending a packet from port 50272 of IP address 192.168.122.100 that is going to port 80 of IP address 81.179.179.69 using IP protocol 6.
- C. IP address 192.168.122.100/50272/81.179.179.69/80/6 is sending a packet from port 80 of IP address 192.168.122.100 that is going to port 50272 of IP address 81.179.179.69 using IP protocol 6.7E503B693763E0113BE0CD2E4A16C9C4
- D. IP address 179.179.69/50272/192.168.122.100/80/6 is sending a packet from port 50272 of IP address 192.168.122.100 that is going to port 80 of IP address 81.179.179.69 using IP protocol 6.
Answer: B
NEW QUESTION 14
Refer to the exhibit.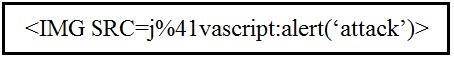
Which kind of attack method is depicted in this string?
- A. cross-site scripting
- B. man-in-the-middle
- C. SQL injection
- D. denial of service
Answer: A
NEW QUESTION 15
Which principle is being followed when an analyst gathers information relevant to a security incident to determine the appropriate course of action?
- A. decision making
- B. rapid response
- C. data mining
- D. due diligence
Answer: A
NEW QUESTION 16
What does cyber attribution identity in an investigation?
- A. cause of an attack
- B. exploit of an attack
- C. vulnerabilities exploited
- D. threat actors of an attack
Answer: D
NEW QUESTION 17
Which access control model does SELinux use?
- A. RBAC
- B. DAC
- C. MAC
- D. ABAC
Answer: C
NEW QUESTION 18
An offline audit log contains the source IP address of a session suspected to have exploited a vulnerability resulting in system compromise.
Which kind of evidence is this IP address?
- A. best evidence
- B. corroborative evidence
- C. indirect evidence
- D. forensic evidence
Answer: B
NEW QUESTION 19
Refer to the exhibit.
Which type of log is displayed?
- A. proxy
- B. NetFlow
- C. IDS
- D. sys
Answer: B
NEW QUESTION 20
......
Thanks for reading the newest 200-201 exam dumps! We recommend you to try the PREMIUM Dumpscollection.com 200-201 dumps in VCE and PDF here: https://www.dumpscollection.net/dumps/200-201/ (98 Q&As Dumps)