Practical of 200-201 answers materials and vce for Cisco certification for client, Real Success Guaranteed with Updated 200-201 pdf dumps vce Materials. 100% PASS Understanding Cisco Cybersecurity Operations Fundamentals exam Today!
Also have 200-201 free dumps questions for you:
NEW QUESTION 1
Which two elements are assets in the role of attribution in an investigation? (Choose two.)
- A. context
- B. session
- C. laptop
- D. firewall logs
- E. threat actor
Answer: AE
NEW QUESTION 2
What is a difference between SOAR and SIEM?
- A. SOAR platforms are used for threat and vulnerability management, but SIEM applications are not
- B. SIEM applications are used for threat and vulnerability management, but SOAR platforms are not
- C. SOAR receives information from a single platform and delivers it to a SIEM
- D. SIEM receives information from a single platform and delivers it to a SOAR
Answer: A
NEW QUESTION 3
An analyst discovers that a legitimate security alert has been dismissed. Which signature caused this impact on network traffic?
- A. true negative
- B. false negative
- C. false positive
- D. true positive
Answer: B
NEW QUESTION 4
Drag and drop the access control models from the left onto the correct descriptions on the right.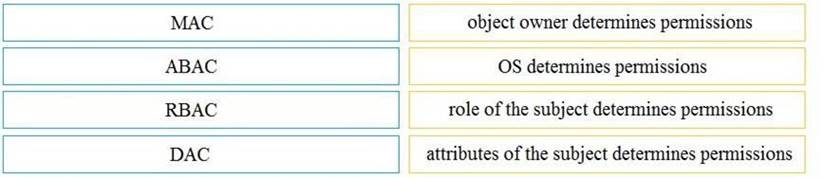
- A. Mastered
- B. Not Mastered
Answer: A
Explanation: 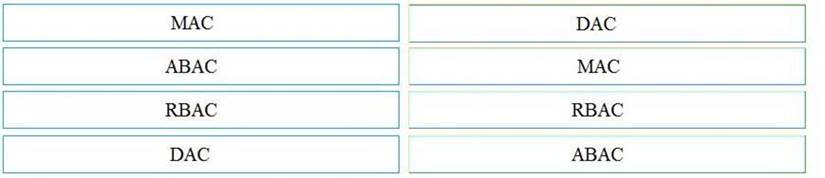
NEW QUESTION 5
The target web application server is running as the root user and is vulnerable to command injection. Which result of a successful attack is true?
- A. cross-site scripting
- B. cross-site scripting request forgery
- C. privilege escalation
- D. buffer overflow
Answer: B
NEW QUESTION 6
Which category relates to improper use or disclosure of PII data?
- A. legal
- B. compliance
- C. regulated
- D. contractual
Answer: C
NEW QUESTION 7
Refer to the exhibit.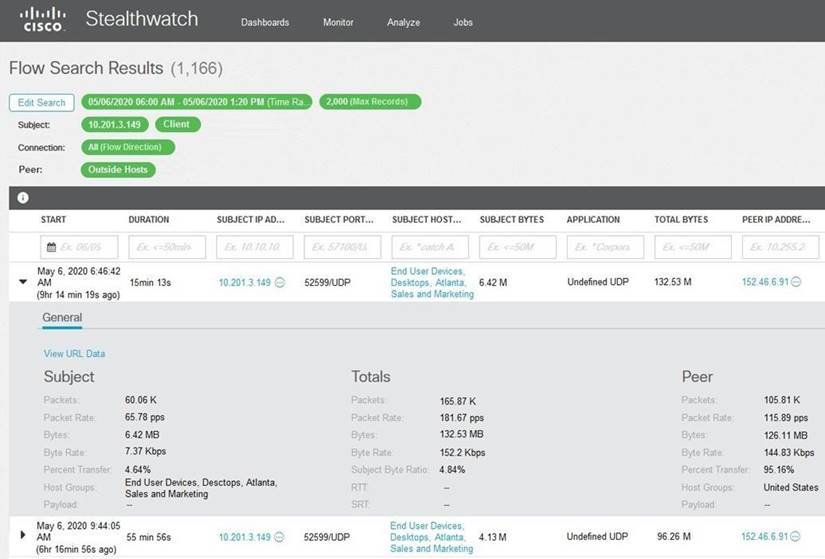
What is the potential threat identified in this Stealthwatch dashboard?
- A. Host 10.201.3.149 is sending data to 152.46.6.91 using TCP/443.
- B. Host 152.46.6.91 is being identified as a watchlist country for data transfer.
- C. Traffic to 152.46.6.149 is being denied by an Advanced Network Control policy.
- D. Host 10.201.3.149 is receiving almost 19 times more data than is being sent to host 152.46.6.91.
Answer: D
NEW QUESTION 8
What is personally identifiable information that must be safeguarded from unauthorized access?
- A. date of birth
- B. driver's license number
- C. gender
- D. zip code
Answer: B
NEW QUESTION 9
Which attack method intercepts traffic on a switched network?
- A. denial of service
- B. ARP cache poisoning
- C. DHCP snooping
- D. command and control
Answer: C
NEW QUESTION 10
What causes events on a Windows system to show Event Code 4625 in the log messages?
- A. The system detected an XSS attack
- B. Someone is trying a brute force attack on the network
- C. Another device is gaining root access to the system
- D. A privileged user successfully logged into the system
Answer: B
NEW QUESTION 11
Which step in the incident response process researches an attacking host through logs in a SIEM?
- A. detection and analysis
- B. preparation
- C. eradication
- D. containment
Answer: A
NEW QUESTION 12
Refer to the exhibit.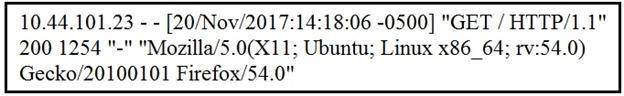
What does the message indicate?
- A. an access attempt was made from the Mosaic web browser
- B. a successful access attempt was made to retrieve the password file
- C. a successful access attempt was made to retrieve the root of the website
- D. a denied access attempt was made to retrieve the password file
Answer: C
NEW QUESTION 13
An engineer runs a suspicious file in a sandbox analysis tool to see the outcome. The analysis report shows that outbound callouts were made post infection.
Which two pieces of information from the analysis report are needed to investigate the callouts? (Choose two.)
- A. signatures
- B. host IP addresses
- C. file size
- D. dropped files
- E. domain names
Answer: BE
NEW QUESTION 14
An analyst is investigating a host in the network that appears to be communicating to a command and control server on the Internet. After collecting this packet capture the analyst cannot determine the technique and payload used for the communication.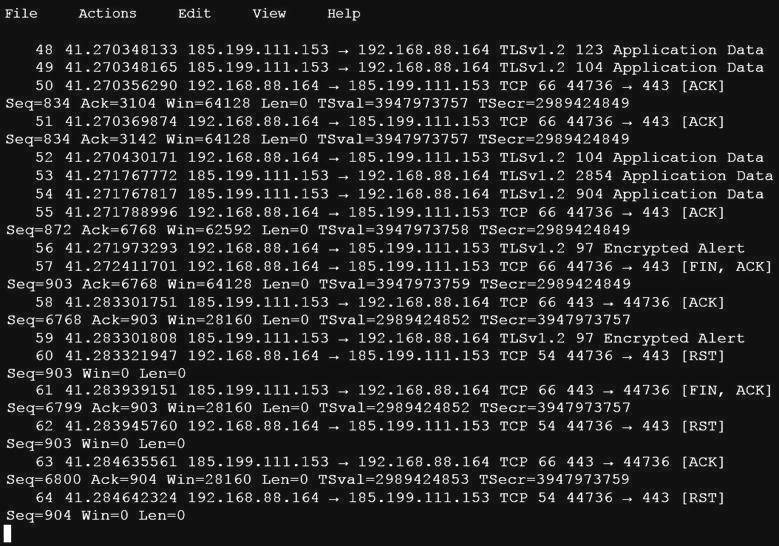
Which obfuscation technique is the attacker using?
- A. Base64 encoding
- B. transport layer security encryption
- C. SHA-256 hashing
- D. ROT13 encryption
Answer: B
NEW QUESTION 15
Which two components reduce the attack surface on an endpoint? (Choose two.)
- A. secure boot
- B. load balancing
- C. increased audit log levels
- D. restricting USB ports
- E. full packet captures at the endpoint
Answer: AD
NEW QUESTION 16
Which regular expression matches "color" and "colour"?
- A. colo?ur
- B. col[08]+our
- C. colou?r
- D. col[09]+our
Answer: C
NEW QUESTION 17
Which signature impacts network traffic by causing legitimate traffic to be blocked?
- A. false negative
- B. true positive
- C. true negative
- D. false positive
Answer: D
NEW QUESTION 18
At which layer is deep packet inspection investigated on a firewall?
- A. internet
- B. transport
- C. application
- D. data link
Answer: C
NEW QUESTION 19
An engineer receives a security alert that traffic with a known TOR exit node has occurred on the network. What is the impact of this traffic?
- A. ransomware communicating after infection
- B. users downloading copyrighted content
- C. data exfiltration
- D. user circumvention of the firewall
Answer: D
NEW QUESTION 20
......
Thanks for reading the newest 200-201 exam dumps! We recommend you to try the PREMIUM DumpSolutions.com 200-201 dumps in VCE and PDF here: https://www.dumpsolutions.com/200-201-dumps/ (98 Q&As Dumps)